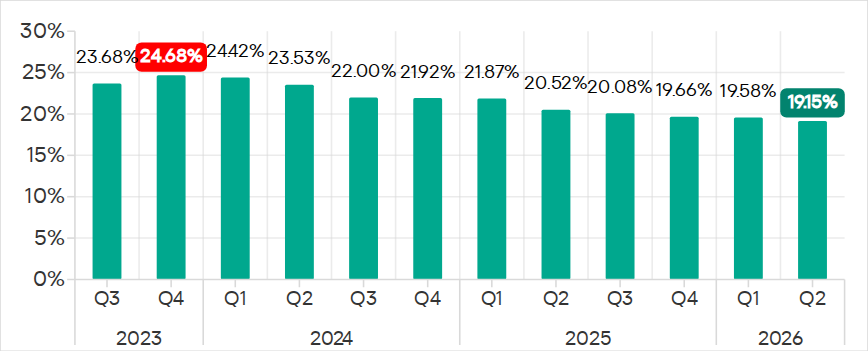Agregátor RSS
Alleged TeamPCP Hackers Charged in Australia Over Major Supply Chain Attacks
The Australian Federal Police (AFP) has charged two Western Australian men with a combined total of 14 offences over their alleged role in TeamPCP, the cybercrime group behind the March 2026 compromise of the open-source security scanners Trivy and Checkmarx KICS and the AI gateway LiteLLM.
Louis Michael Gaebler, 23, and Ruben Ian Thomson, 21, appeared in Perth Magistrates Court on August 27,
Kategorie: Hacking & Security
Alleged TeamPCP Hackers Charged in Australia Over Major Supply Chain Attacks
The Australian Federal Police (AFP) has charged two Western Australian men with a combined total of 14 offences over their alleged role in TeamPCP, the cybercrime group behind the March 2026 compromise of the open-source security scanners Trivy and Checkmarx KICS and the AI gateway LiteLLM.
Louis Michael Gaebler, 23, and Ruben Ian Thomson, 21, appeared in Perth Magistrates Court on August 27, Swati Khandelwalhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
V nové strategii si postavíme virtuální město z Lega. Stojí za ní největší vydavatel žánru
Kategorie: IT News
What the Data Says About AI in Security Operations in 2026
AI is officially mainstream in security operations. According to Prophet Security's State of AI in Security Operations 2026 report (produced from ViB’s survey of 250+ cybersecurity pros), 40% of security teams now use AI daily. Another 56% are currently testing it out, and only 4% have no plans to adopt it.
For the teams already using AI, what is actually changing? Here are the ten biggest
Kategorie: Hacking & Security
What the Data Says About AI in Security Operations in 2026
AI is officially mainstream in security operations. According to Prophet Security's State of AI in Security Operations 2026 report (produced from ViB’s survey of 250+ cybersecurity pros), 40% of security teams now use AI daily. Another 56% are currently testing it out, and only 4% have no plans to adopt it.
For the teams already using AI, what is actually changing? Here are the ten biggest [email protected]
Kategorie: Hacking & Security
Carhartt data breach exposes information of 12.9 million accounts
The ShinyHunters extortion group has published sensitive data from nearly 13 million accounts stolen from clothing retailer giant Carhartt earlier this month, according to data breach notification service Have I Been Pwned. [...]
Kategorie: Hacking & Security
Nuisance-call blocker fined £190k for being a nuisance caller
The UK’s data protection watchdog has fined a nuisance call blocking biz £190,000 ($258,000) for bombarding elderly people with hundreds of thousands of - you guessed it - nuisance calls. Elderly Aids Ltd made 758,053 unsolicited direct marketing calls between May 27, 2024, and February 10, 2025, according to the Information Commissioner’s Office (ICO). On average, that works out as 2,916 calls per day. Busy fingers. The ICO and Telephone Preference Service (TPS), a UK service to register one’s phone number to exclude it from unwanted marketing calls, received 20 complaints during this timeframe related to Elderly Aids. It is illegal for direct marketers to call a number registered with the TPS, unless the individual has given explicit consent to that specific company to call them. All 758,053 unsolicited direct marketing calls, in this case, were made to phone numbers registered with the TPS and belonged to people who had not given their consent for Elderly Aids to contact them. Complainants commonly cited aggressive and misleading sales tactics, with callers also failing to identify themselves. One said their father was pressured into signing up to Elderly Aids’ services, which required a £139 ($188) sign-up fee, and a recurring monthly £6.99 ($9.50) payment on top of this. Andy Curry, head of investigations at the ICO, said: “Not only did this company target vulnerable people who had explicitly asked not to be called – they harassed them to sell call-blocking devices. “EAL showed a complete disregard for the law and the people they were hounding. This penalty should serve as a clear warning to any business that thinks the law does not apply to them - we will hold them to account for both exploiting people in this way and trying to avoid accountability.” Russell Roach, director of preference services at the Data & Marketing Association (DMA), concurred and encouraged responsible businesses to screen their calling lists against the TPS and Corporate TPS (CTPS) registers. “People register with the Telephone Preference Service because they want greater control over who can contact them,” he said. “Cases like this demonstrate why those protections are so important. “Anyone making live marketing calls must respect the choices people have made about their privacy. When organizations ignore those preferences and contact individuals who have explicitly opted out of receiving unsolicited sales calls, particularly those who are most vulnerable, they undermine consumer trust and risk causing significant nuisance and distress.” The ICO said Elderly Aids failed to engage with the regulator, ignoring requests for information, while continuing to make illegal marketing calls. According to public Companies House filings, the company attempted to strike itself off the register three months after it started pestering the elderly with its phone calls, although this was swiftly suspended following an objection. The ICO said that in cases where a debtor cannot pay a fine, such as those in “genuine financial hardship,” they provide payment plans. Organizations that can pay don’t face formal recovery action, and when directors attempt to skirt fines through insolvency, insolvency practitioners are called in, potentially kickstarting a multi-year recovery process. ®
Kategorie: Viry a Červi
Spark RAT Targets Cambodia, Abuses Vulnerable OPSWAT Driver to Disable Security Tools
Individuals and organizations in Cambodia have emerged as the target of a new campaign that delivers an open-source remote access trojan (RAT) called Spark RAT.
"The samples employ diverse lure themes, suggesting an effort to appeal to a broad range of potential victims. These include government notices, public health materials, real estate-related content, and other topics," Acronis Threat
Kategorie: Hacking & Security
Spark RAT Targets Cambodia, Abuses Vulnerable OPSWAT Driver to Disable Security Tools
Individuals and organizations in Cambodia have emerged as the target of a new campaign that delivers an open-source remote access trojan (RAT) called Spark RAT.
"The samples employ diverse lure themes, suggesting an effort to appeal to a broad range of potential victims. These include government notices, public health materials, real estate-related content, and other topics," Acronis Threat Ravie Lakshmananhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Hraní na Linuxu roste. Zoner a Alza lákají na vlastní herní sestavy se systémem Bazzite
Podíl hráčů s linuxovými distribucemi roste, tahounem je SteamOS. • Český Zoner prodává miniPC postavené na distribuci Bazzite. • Hrát je možné hned po instalaci systému, není třeba zdlouhavé nastavování.
Kategorie: IT News
Threat landscape for industrial automation systems. Q2 2026
All threats
In Q2 2026, the percentage of ICS computers on which malicious objects were blocked continued to decrease, falling to 19.15%, its lowest level since 2022.
Percentage of ICS computers on which malicious objects were blocked, Q3 2023–Q2 2026
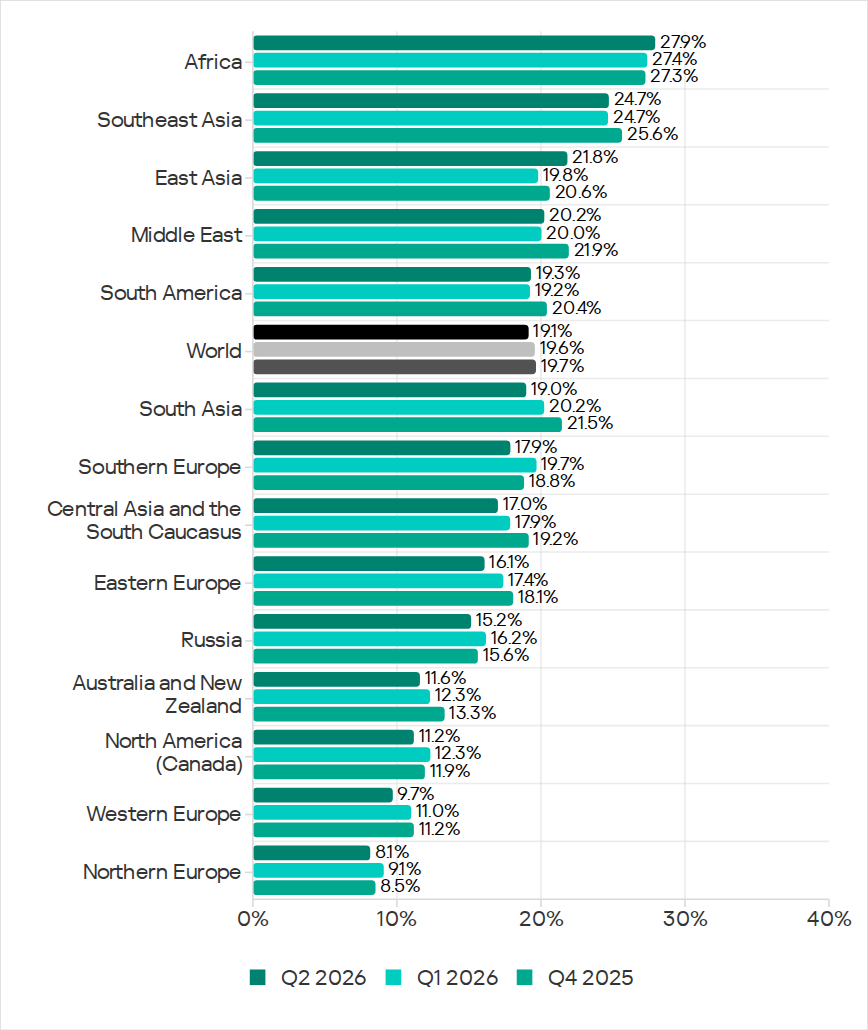
Regionally, the percentages ranged from 8.1% in Northern Europe to 27.9% in Africa.
Regions ranked by percentage of attacked ICS computers
The figures increased in five regions over the quarter, most notably in East Asia (by 2.0 pp) and Africa (by 0.5 pp).
East Asia saw increases in percentages for all threats except miners. The region ranked first in terms of growth for malicious scripts and phishing pages, spyware, and viruses. East Asia also led in terms of growth in threats from the internet. The percentage of ICS computers on which email threats were blocked also increased.
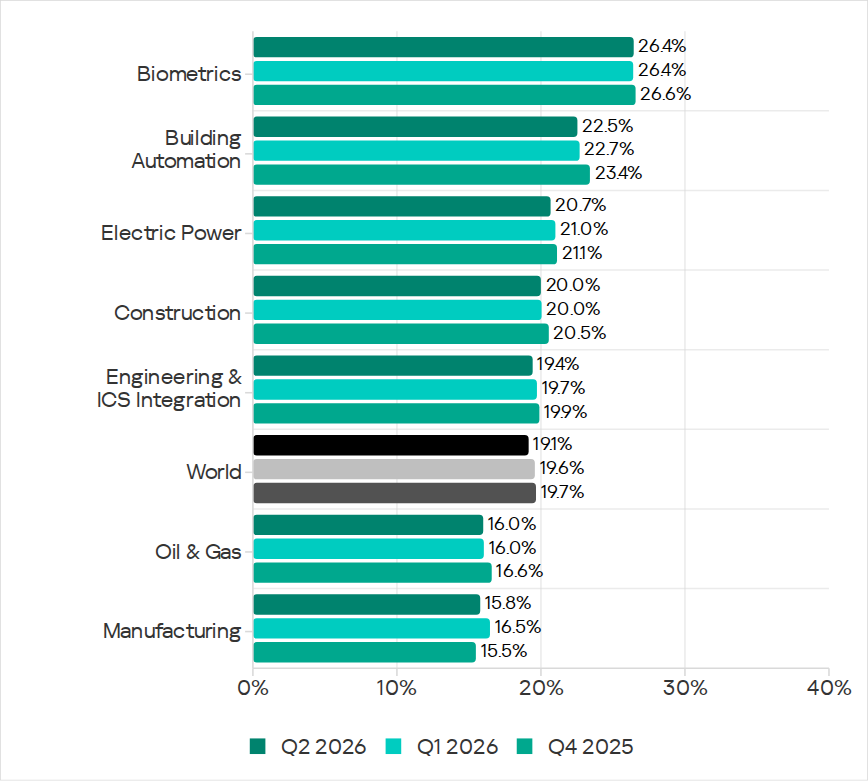
Selected industriesThe biometrics sector (26.44%) has traditionally led the rankings of industries and OT infrastructures surveyed in this report in terms of the percentage of ICS computers on which malicious objects were blocked. Biometric systems are characterized by the availability of internet access, extensive email use for data exchange and approvals (e.g. access granting), and, in many cases, minimal cybersecurity controls within the organizations that use them.
Industries ranked by percentage of ICS computers on which malicious objects were blocked
The biometrics sector ranked first among industries in terms of the following threat categories: malicious scripts and phishing pages, malicious documents, spyware, ransomware, and worms. The sector is also leading among industries in terms of email threats. At the same time, unlike other industries, the percentage of affected ICS computers for email threats in biometrics exceeds that for internet threats.
In all selected industries, the global average follows a downward trend.
Threat categoriesIn Q2 2026, Kaspersky security solutions blocked malware from 10,904 different malware families of various categories on industrial automation systems.
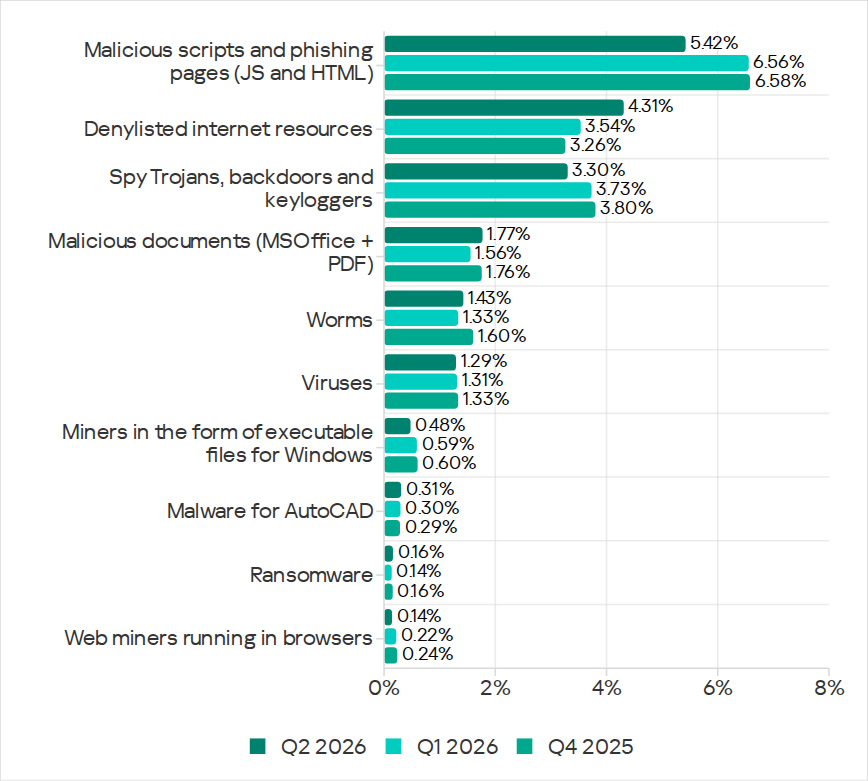
Over the quarter, the percentage of ICS computers on which malicious objects of the following categories were blocked increased: denylisted internet resources, malicious documents, worms, ransomware, and malware for AutoCAD.
Percentage of ICS computers on which the activity of malicious objects from various categories was blocked
Malicious scripts and phishing pages (JS and HTML)Malicious scripts and phishing pages remained in first place in the threat category rankings based on the percentage of ICS computers on which the respective threats were blocked. In Q2 2026, the global average dropped to 5.42%.
Over the quarter, the figure for this category only increased in East Asia, rising by 0.93 pp to 4.86%. This is the second-highest figure in the region in the last three years.
In East Asia, the percentage of ICS computers affected by malicious scripts and phishing pages increased in all the industries surveyed, except construction. The highest figures were recorded for biometrics (9.01%) and building automation (6.49%).
Denylisted internet resourcesIn Q2 2026, denylisted internet resources rose in the threat category rankings from third to second place, displacing spyware. Globally, the percentage of ICS computers on which denylisted internet resources were blocked has been increasing for two quarters in row and reached 4.31%.
The figures increased in all regions over the quarter, most notably in Russia (by 1.33 pp). Moreover, Russia ranked first (5.17%) among the regions in terms of denylisted internet resources. Since 2022, the region has topped these rankings twice before, both times in Q2: in 2022 and 2024.
Among the selected industries in Russia, the highest figures for the denylisted internet resources were in the electric power (6.61%) and engineering and ICS integration (5.62%) industries.
Malicious documents (MSOffice + PDF)Malicious documents ranked fourth in the threat category rankings by the percentage of ICS computers on which they were blocked. The percentage for this category decreased over the previous three quarters, reaching its lowest level in three years. However, in Q2 2026, it increased to 1.77%.
Over the quarter, the figures for malicious documents increased in seven regions, most notably in South America (by 1.35 pp) and Southern Europe (by 0.48 pp). These two regions are among the top three in terms of malicious documents, malicious scripts and phishing pages, as well as threats from email clients.
South America ranked second in the rankings of regions in terms of malicious documents. In Q2 2026, the percentage of ICS computers in the region on which this threat was blocked was 3.56%, which was the fourth highest in three years.
Among the selected industries in South America, the highest percentage of ICS computers on which malicious documents were blocked was in biometrics (6.67%).
Southern Europe ranked first in the rankings of regions in terms of malicious documents. In the previous quarter, the percentage of ICS computers in the region on which this threat was blocked was the lowest in three years, but in Q2 2026 it increased to 3.63%.
Among the selected industries in Southern Europe, the highest percentage of ICS computers on which malicious documents were blocked was once again in biometrics (11.48%).
SpywareSpyware ranked third in the threat category rankings based on the percentage of ICS computers on which it was blocked. The percentage for this category (3.30%) is the lowest since 2022.
Over the quarter, the figures increased in three regions, most notably in East Asia (by 0.53 pp) and Southeast Asia (by 0.42 pp).
East Asia ranked third based on the figures for spyware (4.77%), behind Africa and Southeast Asia. This is the region’s highest rate since Q2 2025. Among the countries and territories in the region, the highest percentage of ICS computers on which spyware was blocked was in mainland China (6.61%). Among the selected industries in East Asia, the highest figures for spyware were in the electric power (11.75%) and manufacturing (5.87%) industries. In all the industries surveyed, the figures are higher than the regional average.
Southeast Asia ranked second after Africa in the ranking of regions in terms of spyware, with 5.32%. Among the selected industries in Southeast Asia, the highest figures for spyware were in biometrics (8.93%) and manufacturing (7.32%). The figures increased in all industries over the quarter.
RansomwareThe percentage of ICS computers on which ransomware was blocked decreased in the previous three quarters but increased to 0.16% in Q2 2026.
During the quarter, the percentage increased in all regions, except Western and Southern Europe and North America (Canada). Africa led the ranking in terms of growth for this metric.
In Q2 2026, Africa ranked first among the regions in terms of the percentage of ICS computers on which ransomware was blocked (0.29%). The only time the figure in the region was higher in the past three years was Q2 2025 (0.31%).
Among the selected industries in Africa, the highest figures for ransomware were in the electric power industry (0.72%) and biometrics (0.52%). Over the quarter, the figures increased in all industries, except manufacturing and construction. The biggest increase was recorded in the electric power industry.
In Russia, the percentage of ICS computers on which ransomware was blocked in biometric systems has increased for three consecutive quarters, reaching 1.22%. This is the highest level of ransomware across all industries in all regions.
MinersIn Q2 2026, the percentage of ICS computers on which miners were blocked was the lowest since 2021, for both miners in the form of executable files for Windows (0.48%) and web miners running in browsers (0.14%).
The figures for both categories decreased in all regions, except for Africa where figures for miners in the form of executable files for Windows increased slightly.
On average, the oil and gas industry led the rankings among the selected industries both in terms of miners in the form of executable files for the Windows OS (0.66%) and in terms of web miners (0.34%).
WormsIn Q2 2026, the percentage of ICS computers on which worms were blocked increased to 1.43%.
In Q2 2026, the Middle East (2.11%) was second (after Africa) in the rankings of regions in terms of worms, displacing Central Asia and the South Caucasus.
Among the selected industries in the Middle East, the highest percentage of ICS computers on which worms were blocked was in building automation (2.90%). Over the quarter, the figures increased in all industries.
Australia and New Zealand ranked 12th among the regions in terms of the percentage of ICS computers on which worms were blocked (0.41%). Over the past three years, the figure in this region was only higher in Q2 2024 (0.42%). The figures increased in all the surveyed industries in the region, most notably in manufacturing and electric power. As a result, for these industries they exceeded the regional average by 2.9 and 2.3 times, respectively.
VirusesIn Q2 2026, the percentage of ICS computers on which viruses were blocked decreased to 1.29%.
The top three regions for this metric remain unchanged: Southeast Asia (6.03%), Africa (4.22%), and East Asia (3.14%). These same regions lead the rankings in terms of malware for AutoCAD.
The figures increased in three regions: East Asia, Australia and New Zealand, and Africa, where it has been growing for four consecutive quarters and reached its highest value since 2022.
Among the selected industries in Africa, the highest percentage of ICS computers on which viruses were blocked was in construction (5.47%).
East Asia ranked third among the regions in terms of viruses, reaching the highest level in the region for the past three years. Among the countries and administrative regions of East Asia, mainland China is the clear leader in terms of viruses (5.07%).
Among the selected industries in East Asia, the highest percentage of ICS computers on which viruses were blocked was in construction (5.93%).
In Australia and New Zealand, the increase in the percentage of ICS computers on which viruses were blocked was primarily due to a 4.3-fold increase in the figure for the electric power industry: from 0.29% to 1.24%. For a region where the percentage of attacked ICS computers for all threats is 0.12%, this is a very high value.
Malware for AutoCADIn Q2 2026, the percentage of ICS computers on which malware for AutoCAD was blocked increased to 0.31%.
The most notable increase over the quarter was observed in Africa. After more than doubling in the previous quarter, the figure for the region continued to rise (although not so dramatically), reaching 1.02%.
Among the selected industries across all regions, the highest percentage of ICS computers on which malware for AutoCAD was blocked was in construction in East Asia (6.38%) and in Southeast Asia (4.05%).
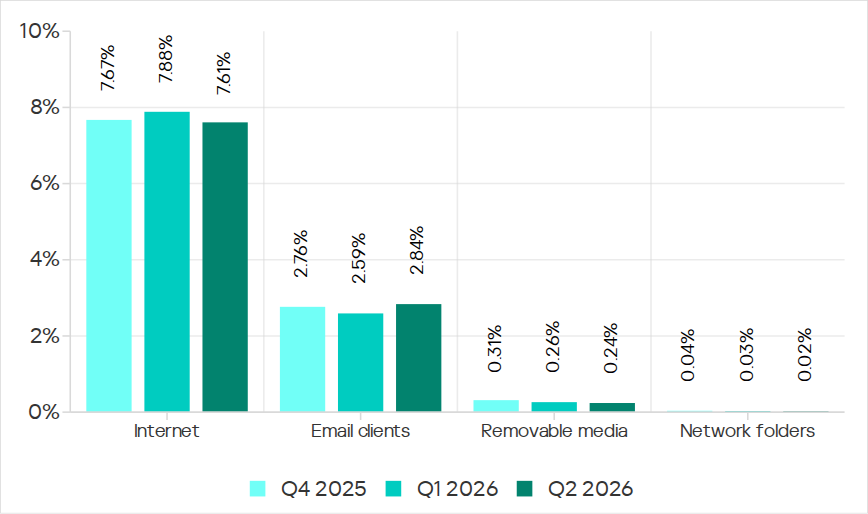
Main threat sourcesIn Q2 2026, of all the threat sources, the percentage increased only for email.
Percentage of ICS computers on which malicious objects from various sources were blocked
InternetThe percentage of ICS computers on which threats from the internet were blocked decreased to 7.61%, reaching its lowest level since 2021.
Over the quarter, the percentage increased in three regions: East Asia by 0.8 pp (to 6.3%), South Asia by 0.3 pp (to 10.4%), and Russia by 0.3 pp (to 6.4%).
Among the selected industries across all regions, the highest percentage of ICS computers on which threats from the internet were blocked was in biometrics (13.03%) and engineering and ICS integration (12.16%) in South Asia.
EmailThe percentage of ICS computers on which email threats were blocked increased to 2.84%.
In Q2 2026, the percentage of ICS computers on which email threats were blocked increased in South America by 1.0 pp (to 5.2%) and in Africa by 0.7 pp (to 4.3%).
Among the selected industries across all regions, the highest percentage of ICS computers on which email threats were blocked was in biometrics (19.14%) and building automation (12.49%) in Southern Europe.
Removable mediaThe percentage of ICS computers on which threats from removable media were blocked continued to decrease, reaching 0.24%, the lowest value for the period under review.
Among the selected industries across all regions, the highest percentage of ICS computers on which threats from removable media were blocked was in the electric power industry in East Asia (1.34%) and biometrics in Africa (1.29%).
Network foldersThe percentage of ICS computers on which threats from network folders were blocked continued to decrease. In Q2 2026, it was the lowest for the period under review, at 0.023%.
The only region to see an increase in the percentage of ICS computers on which threats from network folders were blocked during the quarter was Africa. This was mainly due to an increase in the building automation figure to 0.05%.
Among the selected industries across all regions, the highest percentage of ICS computers on which threats from network folders were blocked was in biometrics (0.23%), building automation (0.17%), and engineering and ICS integration (0.13%) in East Asia.
For more information on industrial threats see the full version of the report.
Kategorie: Hacking & Security, Viry a Červi
Nepálské údolí smetlo unikátní horské tsunami. USGS už zná viníka přírodní katastrofy (video)
Během středy se na sociálních sítích začaly šířit zprvu nepotvrzené záběry masivní přívalové povodně v Nepálu, která ničila celé vesnice.
Svojí sílou se vymykala běžným obrazům podobných přírodních katastrof z horských oblastí Asie, a tak ji mnozí zpočátku považovali za dílo AI. Zvláště pak ...
Kategorie: IT News
GoCaracal Malware Uses Ethereum Smart Contract to Fetch Replacement C2 Address
Threat actors linked by Arctic Wolf to Dark Caracal with medium confidence deployed a previously undocumented Go-based malware framework, GoCaracal, during a June 2026 intrusion at an unnamed communications organization in Venezuela.
GoCaracal provides operators with remote shell access and payload execution, while the extended profile adds browser data theft, keylogging, remote desktop control
Kategorie: Hacking & Security
GoCaracal Malware Uses Ethereum Smart Contract to Fetch Replacement C2 Address
Threat actors linked by Arctic Wolf to Dark Caracal with medium confidence deployed a previously undocumented Go-based malware framework, GoCaracal, during a June 2026 intrusion at an unnamed communications organization in Venezuela.
GoCaracal provides operators with remote shell access and payload execution, while the extended profile adds browser data theft, keylogging, remote desktop controlSwati Khandelwalhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
CISA orders feds to patch Citrix NetScaler RCE flaw by Saturday
CISA has ordered U.S. government agencies to patch their Citrix NetScaler appliances against an actively exploited remote code execution vulnerability by Saturday. [...]
Kategorie: Hacking & Security
Nejlevnější věc od Applu stojí jen 250 Kč. Vysmívaný hadřík se vrací v nové verzi
Všechno ostatní Apple zdražil, ale jeden produkt naopak zlevnil o 68 %. Čisticí hadřík se po pěti letech vrátil v nové verzi. Už ale nestojí přemrštěných 590 Kč jako předchozí verze, ale jen 250 Kč. Jde tak o nejlevnější věc, kterou Apple prodává.
Firma nepopisuje, co se změnilo. Spekulovalo se ...
Kategorie: IT News
ATF confirms “major incident” after recent Qilin breach claims
ATF, the regulatory agency that enforces federal laws governing firearms and explosives in the United States, has confirmed that one of its systems was compromised after breach claims made by the Qilin ransomware gang. [...]
Kategorie: Hacking & Security
New GPUThor Rowhammer Defeats ECC on NVIDIA RTX A6000 to Gain Host Root Access
Academic researchers have disclosed a Rowhammer attack impacting NVIDIA workstation GPUs with GDDR6 memory that defeats error correction codes (ECC), the mitigation NVIDIA recommends against GPU Rowhammer, and enables denial-of-service (DoS) and privilege escalation to a root shell.
Dubbed GPUThor, the attack was developed by researchers at the University of Toronto, who hammered four DRAM
Kategorie: Hacking & Security
New GPUThor Rowhammer Defeats ECC on NVIDIA RTX A6000 to Gain Host Root Access
Academic researchers have disclosed a Rowhammer attack impacting NVIDIA workstation GPUs with GDDR6 memory that defeats error correction codes (ECC), the mitigation NVIDIA recommends against GPU Rowhammer, and enables denial-of-service (DoS) and privilege escalation to a root shell.
Dubbed GPUThor, the attack was developed by researchers at the University of Toronto, who hammered four DRAM Swati Khandelwalhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Staronová GeForce RTX 3060 už je podstatně dražší než rychlejší GeForce RTX 5050
Vývoj cen v posledních týdnech posunul GeForce RTX 3060 na úroveň, při které o ní nemá smysl uvažovat nejen oproti nabídce konkurenčních značek, ale ani při srovnání se současnou generací od Nvidie…
Kategorie: IT News
- « první
- ‹ předchozí
- …
- 68
- 69
- 70
- 71
- 72
- 73
- 74
- 75
- 76
- …
- následující ›
- poslední »