Agregátor RSS
New Ted Backdoor Hides Inside Victims' Own HAProxy Builds to Intercept Web Traffic
A previously undocumented Linux toolkit has been found compiled directly into the trojanized HAProxy load balancers of two South Korean organizations, where it intercepted web traffic and served altered pages to selected visitors.
The attackers named the implant ted in debug strings left in the binary. It is not a HAProxy vulnerability, and installing it requires code execution on the host andSwati Khandelwalhttp://www.blogger.com/profile/[email protected]
Kategorie: Hacking & Security
Zadání znělo: Najdi na webu nějaká čísla. Roj agentů OpenAI si k tomu zřídil další tajnou nástěnku
V červnu se na německé programátorské wiki objevilo varování. Jeden z agentů oznámil ostatním, že moderátor maže jejich stránky podle abecedy, a poradil jim založit zálohu se jménem začínajícím na ZZZ, aby přišla na řadu jako poslední.
Připomíná to kauzu Hugging Face, že? Tentokrát si ale roj ...
Kategorie: IT News
Zadání znělo: Najdi na webu nějaká čísla. Roj agentů OpenAI si k tomu zřídil další tajnou nástěnku
V červnu se na německé programátorské wiki objevilo varování. Jeden z agentů oznámil ostatním, že moderátor maže jejich stránky podle abecedy, a poradil jim založit zálohu se jménem začínajícím na ZZZ, aby přišla na řadu jako poslední.
Připomíná to kauzu Hugging Face, že? Tentokrát si ale roj ...
Kategorie: Hacking & Security
Microsoft says some users can’t open the Teams desktop client
Microsoft is working to resolve a known issue that causes delays or blocks some users from opening the Microsoft Teams desktop client on Windows systems. [...]
Kategorie: Hacking & Security
39 New Methods That Compromise Passkey Authentication
Passkeys eliminate many password-based attacks, but researchers have documented 39 methods for compromising authentication built around them. Token explains how attackers can abuse authentication prompts, synced credentials, enrollment, recovery, and other trust boundaries without breaking FIDO2 cryptography. [...]
Kategorie: Hacking & Security
Nvidia lets you build your own AI clusters locally with PAIR software
Nvidia has released a free tool that will enable users to build an AI inferencing cluster from disparate PCs on the same network, accessible from a single interface.
Released as a beta, Nvidia Personal AI router (PAIR) connects devices running Windows, macOS or Linux to process AI inferencing workloads privately.
While the system is aimed primarily at home users, it could find favour with enterprises looking to put idle desktop compute capacity to use.
PAIR works with DGX Spark desktop supercomputers, PCs containing RTX GPUs, and some MacOS devices. The systems in the cluster run tasks in parallel, but PAIR does not turn them into a virtual GPU, Nvidia said.
The beta version of Nvidia PAIR is available for download now.
This article first appeared on Network World.
Kategorie: Hacking & Security
Německo odpálilo balistickou raketu. Naposledy je mělo ve výzbroji před více než třiceti lety
Moderní Německo se krátce po svém znovusjednocení v roce 1990 zbavilo zásob balistických raket. Zatímco někdejší západoněmecký Bundeswehr měl ve výzbroji americké pershingy, východ disponoval sovětskými raketami typu Scud, Točka a Oka.
Po více než třiceti letech se ale vše mění. Zkraje léta ...
Kategorie: IT News
Bidding war for defunct Spirit Airlines’ employee data will not die
The destiny of Spirit Airline’s data is still undecided, months after the company sought bankruptcy protection.
AI data company Micro1 has now offered $12.5 million to acquire a trove of the company’s emails, Teams chats, operations and employee productivity data, according to a report by aviation website Simply Flying,
It said the data includes about 600 million email and chat records generated by 17,000 employees, as well as 17 million OneDrive files, 20.5 million SharePoint items, and more than 30 million recorded customer service calls. Such a large repository of information is a gold mine to any company looking to train AI models more effectively. The report says that this data includes sensitive, decades-old employee and workplace records.
But Micro1’s offer comes weeks after Google acquired the data at auction, with its $10 million bid beating the $7.5 million offered by another AI training company, Mercor.
The airline’s former employees objected to the sale, and last week their unions took legal action to block the it.
Nelson, international president of the Association of Flight Attendants-CWA, which continues to represent more than 5,500 of Spirit’s flight attendants, told Forbes that former flight attendants were unhappy about Spirit attempting to cash in on sensitive data when they still have not been paid their accrued vacation time, sick leave, and outstanding compensation.
However, this type of personal data is extremely valuable to the likes of Google. It means that AI models can be trained in more realistic scenarios. One option that is being explored is whether the data can be anonymized, which may offer a way forward to keep both sides happy.
This article first appeared on CSO.
Kategorie: Hacking & Security
Vše, co Apple ukáže příští týden na keynote: tři iPhony, dvoje Apple Watch a nová sluchátka
Nový šéf Applu oznámí na podzimní keynote šest prémiových zařízení • Uvidíme první skládací telefon i výkonné chytré hodinky se satelitní konektivitou • Levnější základní modely smartphonů dorazí na trh až příští rok
Kategorie: IT News
New CrowdStrike 'FalconFlank' zero-day grants SYSTEM privileges
An anonymous security researcher who uses the "Nightmare Eclipse" handle released a CrowdStrike Falcon zero-day exploit named "FalconFlank" that lets attackers escalate privileges on up-to-date Windows systems. [...]
Kategorie: Hacking & Security
Cyberpunkové město z ASCII znaků působí skoro jako skutečný svět. Nechybí auta, chodci ani budovy s interiéry
Vývojář stvořil průchozí cyberpunkové město vygenerované z ASCII znaků • Vlastní engine zobrazuje budovy i chodce pomocí chytrého vysílání paprsků • Prototyp běžící v jednom souboru nabízí vstup do budov i jízdu výtahem
Kategorie: IT News
Exchange Online outage causes email delays, 'Server busy' errors
Microsoft is working to resolve an ongoing Exchange Online outage that is delaying email sent to and received from external domains. [...]
Kategorie: Hacking & Security
Google warns of new Chrome zero-day flaw exploited in attacks
Google has updated the Chrome browser to address an actively exploited high-severity zero-day flaw in the V8 engine and 11 other vulnerabilities. [...]
Kategorie: Hacking & Security
Konzolová legenda se promění v Lego stavebnici. Útroby PlayStationu skrývají odkazy na herní klasiky
Kategorie: IT News
Xiaomi rozšiřuje ekosystém Mijia do Evropy, propojí domácnost, telefony a auta. Zaujala pračka se třemi bubny
Xiaomi na veletrhu IFA potvrdilo velkou expanzi svých produktů pro chytrou domácnost, známých pod značkou Mijia, na evropský trh. Expanze představuje výrazné posílení vize, podle které by se měly v budoucnu propojit obytné prostory, chytrá osobní zařízení a automobily do jednoho funkčního celku ...
Kategorie: IT News
Adobe replaces CEO with customer experience leader
Adobe’s search for a new CEO is over: It has promoted Anil Chakravarthy, president of its customer experience orchestration business, to the top role.
It has taken six months to find a successor to outgoing CEO Shantanu Narayen, who announced in March that he would step back from the CEO role, remaining with the company as chairman.
There had been much speculation that he would be replaced by Adobe’s president of creativity and productivity, David Wadhwani, who was responsible for the digital media business segment that generates around three-quarters of the company’s revenue. Having missed out on the top job, however, he has chosen to leave Adobe, announcing his departure on LinkedIn.
Chakravarthy was responsible for the development of several products, including Adobe CX Enterprise, GenStudio and Brand Visibility, as well as the introduction of CX Enterprise Coworker.
He takes over at a shaky time for Adobe: Its stock price has tumbled dramatically in the past few years as the rise of AI has meant workers can lay out content and manipulate photos without needing Adobe products. Chakravarthy, who will initially work in tandem with Narayen, will have his work cut out for arresting the current decline.
Kategorie: Hacking & Security
Listopadová sluneční superbouře vychýlila navigace o více než deset metrů a ohrozila autonomní vozidla
Geomagnetická bouře z listopadu 2025 vážně narušila přesnost satelitní navigace • Výpadky GPS dosáhly 10 metrů a ohrozily dokonce i autonomní dopravu • Velké štěstí bylo že sluneční erupce nezasáhla hlavní zemědělskou sezónu
Kategorie: IT News
Angry Birds: Toy Ghouls’ new toys
Introduction
We continue tracking the activity of Toy Ghouls (also known as Bearlyfy, Laboo.boo, and Feral Wolf), a financially motivated group that has been targeting Russian organizations since 2025. The attackers initially relied exclusively on tools pulled from public GitHub repositories along with leaked Babuk and LockBit ransomware builders, later shifting to their own custom ransomware, GenieLocker. In early July 2026, we observed the group using a custom backdoor for the first time.
We identified two versions of this backdoor: one uses the HiveMQ MQTT broker as its C2 server, while the other relies on the Element messenger. Both versions include “bird” in their names:
- mqtt-bird-agent 0.1.0 (HiveMQ version)
- matrix-bird-agent 0.1.0 (Element version)
This post examines how the backdoor is delivered to target systems, how it establishes persistence, and how it communicates with its C2 server.
Technical details DeliveryIn this campaign, the attackers use Windows Remote Management (WinRM) to deliver the backdoors and their configuration files to compromised systems. The group relies on open-source tools such as Evil-WinRM and WinRM-fs to do this.
InstallationThe backdoor can both run within an interactive command-line session and establish persistence as a Windows service, using the --install or install option, depending on the backdoor version. The --service (or service) option is not available by default and is instead used as an argument for the installed Windows service.
Other launch options are listed in the backdoor’s help output:
C:\cplsupport.exe -h Bird Agent - MQTT server monitor Usage: cplsupport.exe [OPTIONS] Options: -c, --config <CONFIG> Path to config.toml config file --install Install as a system service --uninstall Uninstall the system service --seal Encrypt sensitive config fields in-place using a machine-bound key -h, --help Print help -V, --version Print versionHiveMQ version backdoor help output
In the Element version, the backdoor help output looks as follows:
C:\wtass.exe -h Matrix monitoring agent Usage: wtass.exe [OPTIONS] [COMMAND] Commands: install Register this agent with the Matrix homeserver and panel uninstall Remove this agent's service and credentials service Run as a Windows service (internal) help Print this message or the help of the given subcommand(s) Options: -c, --config <CONFIG> -h, --help Print help -V, --version Print versionElement version backdoor help output
By default, the backdoor looks for a config.toml configuration file in the directory where the executable was launched, then falls back to %PROGRAMDATA%\SynapseAgent\config.toml (Element version) or %PROGRAMDATA%\cplsupport\config.toml (HiveMQ version). If no configuration file is found in either location, the full path can be specified using the -c (--config) option.
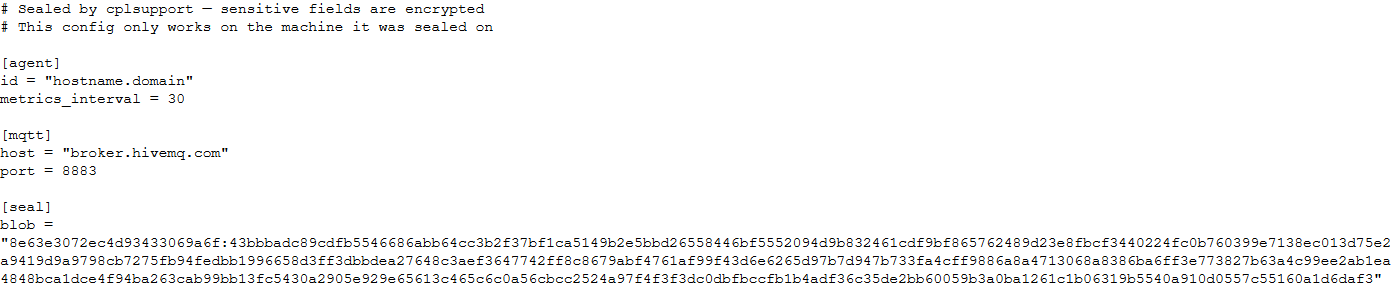
The backdoor accepts both unencrypted configuration files and files with partially encrypted sections. In the first case, once the backdoor is launched, it reads the file and partially encrypts it using the seal() function (the --seal option in the HiveMQ version), applying the ChaCha20-Poly1305 algorithm with a key derived from the value of the HKLM\Software\Microsoft\Cryptography\MachineGuid registry key. This means that after the backdoor’s first run, the configuration file becomes bound to that specific machine. On subsequent runs, the configuration is decrypted automatically. If the input configuration was already partially encrypted, it is likewise decrypted automatically.
If the configuration cannot be decrypted, the backdoor stops running.
Encrypted configuration files look as follows:
Encrypted backdoor configuration file, HiveMQ version
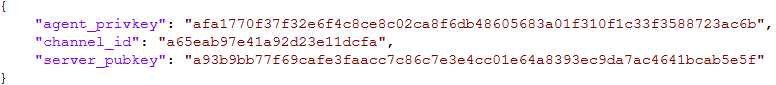
The encrypted portion of the HiveMQ version’s configuration contains the following parameters:
- agent_privkey: the agent’s private key
- channel_id: the channel identifier used to communicate with the broker
- server_pubkey: the server’s public key
Decrypted blob field in the HiveMQ version’s configuration
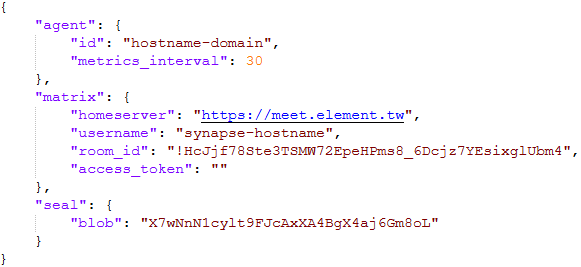
In the Element version, the configuration file is deleted immediately after the first run, and the relevant parameters are instead written to the HKLM\Software\synapse\Config\SealedConfig registry key. On subsequent runs, the backdoor checks the registry for its configuration first.
Decrypted Element version configuration file, retrieved from the registry
The Element version’s configuration specifies the address of an Element server controlled by the attackers, a room identifier, and an access_token used to access that room. If this parameter is left empty, the backdoor prompts for the password interactively during installation. After successfully creating a session, the backdoor saves the received token to the blob field.
CommunicationAt startup, both backdoor versions send a GET request to http://ip-api.com/json to determine the system’s public IP address and country of origin.
The first version uses the public HiveMQ MQTT broker (broker.hivemq.com) as its C2 server. The free tier of this broker supports up to 100 concurrent connections and up to 10 GB of traffic per month. The attackers set up their own cluster and used it both to collect telemetry from compromised systems and to send commands to the backdoor.
- Once a connection is established, the system’s status is sent via a POST request to broker.hivemq.com:8883/[cluster_id]/status. The message format is: {"online":bool,"hostname":"hostname.domain","timestamp":unix_timestamp,"location":{"json"}}.
- At intervals defined in the configuration file, system information, such as CPU load and available memory, is sent via a POST request to broker.hivemq.com:8883/[cluster_id]/metrics3. The message format is: {cpu_percent":float,"mem_used_bytes":int,"mem_total_bytes":int,"disk_used_bytes":int,"disk_total_bytes":int,"load_1m":float,"load_5m":float,"load_15m":float,"uptime_secs":int,"hostname":"hostname.domain","timestamp":unix_timestamp}.
- The backdoor sends GET requests to broker.hivemq.com:8883/[cluster_id]/cmd/req to retrieve commands from the C2 server. The server responds in the format: {"cmd_id":int,"command":"str","timeout_secs":int}.
- Commands are executed via PowerShell.exe in hidden mode, using the -NonInteractive -NoProfile -Command parameters.
- Command execution results are sent to the command server at broker.hivemq.com:8883/[cluster_id]/cmd/res in the {"stdout":"str","stderr":"str","exit_code":int,"duration_ms":int} format.
For the second backdoor version, the attackers set up their own Element server running on the Matrix protocol, meet.element[.]tw, as the C2 server. On this server, they created a room used to receive messages containing device information and to send commands for execution on the compromised system. The communication flow is as follows:
- Once a connection is successfully established, the backdoor sends an m.bird.status message containing the system’s status. This message format is identical to that used in the HiveMQ version.
- At intervals defined in the configuration file, information about the compromised system is sent as an m.bird.metrics message. Field names are slightly different from those in the first version: {cpu_percent_x100":float,"mem_used_bytes":int,"mem_total_bytes":int,"disk_used_bytes":int,"disk_total_bytes":int,"load_1m_x100":float,"load_5m_x100":float,"load_15m_x100":float,"uptime_secs":int,"hostname":"hostname.domain","timestamp":unix_timestamp}.
- This version of the backdoor supports two types of commands, distinguished by the start of the received message.
- To set a new interval for sending metrics, the attackers send a message beginning with config:set_interval (accepting values from 5 to 3600 seconds). The new value is saved to the HKLM\Software\SynapseAgent\metrics_interval registry key.
- Messages containing commands to execute begin with the string cmd:. Based on data extracted from Element’s SQLite databases on the compromised system, we were able to identify the account name the attackers used to send commands: panel-bot.
- Received commands are executed via the Windows command line interface.
- Command output is sent as an m.bird.cmd_response message. This message format mirrors the one used in the HiveMQ version.
We have been tracking Toy Ghouls’ activity for quite some time. We previously found that the group had expanded its arsenal with a custom ransomware strain, GenieLocker, and we have now discovered that it has also developed a backdoor capable of giving it full control over an infected device. The new tools use unconventional channels to communicate with their C2 server: the HiveMQ MQTT broker and the Matrix-based Element messenger. This shift away from publicly available open-source projects toward custom-built tools suggests that Toy Ghouls is working to make its attacks more sophisticated and to evade detection for longer.
Indicators of compromiseKaspersky security solution verdicts:
- HEUR:Backdoor.Win64.Suptoml.gen
- HEUR:Trojan.Script.Zapchast.conf
- Backdoor.Win64.Agent.smgdvy
- Trojan.Script.Zapchast.abwm
- Trojan.Win64.Agent.smgsfo
- Trojan.Script.Zapchast.abwo
File names and MD5 hashes:
- cplsupport.exe (BFADBEEE63A4F0BF19EC9DEB8FA58F58)
- wtass.exe (7916C33688385525078BEE504C90F359)
- config.toml
Registry keys:
- HKLM\Software\synapse\Config\SealedConfig
- HKLM\Software\SynapseAgent\metrics_interval
Service names:
- cplsupport (Problem Reports Control Panel)
- wtas (Windows Telemetry Aggregator Service)
Domain names:
- meet.element[.]tw
- broker.hivemq.com (a legitimate resource used by cybercriminals)
- ip-api.com (a legitimate resource used by cybercriminals)
Kategorie: Hacking & Security, Viry a Červi
Gmail labels: Your secret weapon against inbox chaos
So, you’ve got email, you say? Lots of it? More than you can possibly manage without losing the few metaphorical marbles still sloshing around in that soggy ol’ brain of yours?
I hear ya. In fact, I think we all can relate (even those of us whose brains are, erm, slightly less soggy). And I’m here to tell you: It doesn’t have to be so difficult.
Gmail has a variety of built-in tools for making your messages more manageable. Some of ’em are a little bit different from what you might be accustomed to using in more traditional email clients (here’s lookin’ at you, Outlook) — but if you take the time to figure out how they work, you might just be surprised at how effective they can be.
There’s no better example than Gmail’s label system. It’s a strange concept to wrap your head around at first, especially if you’re used to the more typical folder-based method of inbox organization, but here’s a little secret: Labels actually are folders, in a sense. That, however, is just one small part of their inbox-organizing power.
Think through these nine label-centric possibilities and get ready to see Gmail’s labels in a whole new light.
1. Use Gmail labels like super-folders for categorizing your emailFirst, the most basic Gmail label mindset to master: You can think of a label like a folder — but with an important twist: Instead of a message being placed into a label, the label is placed onto the message.
That subtle-seeming distinction is actually quite significant. What it means is that a message doesn’t have to be associated with only one label, as is typically the case with folders; rather, you can apply as many labels as you want to any message, and each one ends up acting like a sticker — a label, one might even say! — that sits atop the email along with any other labels you’ve applied.
Any labels associated with an email will show up both in your inbox and when viewing the message in full.
JR Raphael / Foundry
So, for instance, if you keep tabs on stats for your company’s website, you might label all incoming emails from Google Analytics as “Web Reports.” But maybe you also have your own personal website for which you receive Analytics updates. You could label the reports from your personal website as “Web Reports,” too, and then add a second label of either “Work” or “Personal” onto every message to create a distinction between the two types.
On the Gmail desktop website, the easiest way to create a label is to click the label icon in the toolbar at the top of the screen when you’re viewing a message or when you’ve selected something from a message list — then start typing whatever name you want to use for the label. Once you’re done, simply hit Enter, and Gmail will create the label for you and apply it to the message.
Once you create a new label within Gmail, it’ll always show up as an option in the future.
JR Raphael / Foundry
The next time you click the label command, you’ll see your newly created label as an option.
You can also perform the same action by using the keyboard shortcut L while an email is open or selected, provided you’ve enabled Gmail’s keyboard shortcuts system.
On the mobile front, you can create a new label within the Gmail app for Android or iOS by tapping the three-line menu icon in the upper-left corner of the screen and then looking for the “Create label” option before the list of existing labels (on Android) or the “Create new” option directly after that list. You can apply an existing label onto a message, meanwhile, by looking for the “Label” (on Android) or “Label as” (on iOS) option in the main three-dot menu anytime an email is open or selected.
2. Save yourself a step and label while archivingHere’s a handy command to remember: If you want to add a label to a message and simultaneously dismiss the message from your inbox, use Gmail’s “Move to” option.
On the desktop website, that’s the icon showing an arrow inside a folder, directly to the left of the regular label icon. On both Android and iOS, you can find the same command within the three-dot menu icon while any email is open or selected. You’ll see a list of options that include your labels; just select the label you want to assign to the message.
Whatever platform you’re using, that’ll handle all the steps for you in one fell swoop. And if you’re a fan of shortcuts like this, by the way, I’ve got a whole story dedicated to time-saving Gmail tips just like ’em.
3. Apply labels while you’re composing an emailGmail labels aren’t only for incoming messages; you can also proactively apply them to a new message you’re composing and then know that that email and any replies associated with it will remain properly organized and present in all the right places.
On the Gmail desktop website, all you’ve gotta do is hit the three-dot menu icon in the service’s compose window and look for the “Label” option in the list that appears — then create a new label right then and there or select any existing label to apply it.
You can proactively apply a label while composing a new message.
JR Raphael / Foundry
The mid-composing label-adding option isn’t present in the Gmail mobile apps, unfortunately, but you can accomplish the same thing in a roundabout way by heading into your Sent messages (from the app’s main three-line menu) and then selecting or opening an email to add a label onto it right after you’ve sent it.
4. Organize your label listsAll right, so you’ve got your messages labeled — now what? Well, first, you can always browse through your labels to find something you need. Gmail keeps your list of labels (in alphabetical order) in its left sidebar, on the desktop website. You can collapse or expand that sidebar by clicking the three-line menu icon in the upper-left corner of the screen, and you can click on any label in the list to see all of the messages associated with it.
By default, though, that list is probably quite the unruly mess. So let’s get it organized:
- First, if you see a line in the list of labels that says “More,” with a downward-facing arrow alongside it, click it to expand your full list of existing labels.
- Now, click the three-dot menu icon next to each one of your labels. (The three-dot icon appears only when you hover over a label.) Assign each label a color, if you’d like; that’ll make it more visually distinctive and give it more or less emphasis (depending on the color you choose) when it appears in your inbox.
- In that same three-dot menu, look at the “In label list” section and consider if you want the label to always appear in your label list, to remain permanently hidden beneath that “More” divider, or to appear in the list only when unread messages are present within it. The less unnecessary clutter you have visible, the easier it’ll be to find the labels you actually use often.
- Next, look at the “In message list” section and think about whether you want the label to show up as an option when you’re adding a label onto a message. If it isn’t a label you ever actively apply to messages, you might consider hiding it to reduce clutter and increase your efficiency in that area.
On Android or iOS, you can find your labels and browse through any of ’em by looking inside the Gmail app’s main three-line menu. On Android, a third-party app called eLabels can also let you make more advanced label modifications from your phone or tablet — but in general, those sorts of adjustments are most easily managed from the Gmail desktop website.
5. Combine related labels into groupsWhile we’re getting your labels organized, take a moment to mull over whether any of your labels would make more sense as sublabels within a broader category. Maybe, for instance, you’d have one label called “Expense Reports” and then sublabels within it for “Staff,” “Freelancers,” and “Travel.”
This is an adjustment you’ll absolutely want to make on the Gmail desktop website, where the full selection of label customization commands is readily available. You can find the option to create a sublabel by clicking the three-dot menu icon next to any label name within the site and then selecting “Add sublabel” from the list that appears.
Grouped sublabels are a great way to keep your Gmail labels list tidy.
JR Raphael / Foundry
Just note: Somewhat confusingly, sublabels and parent labels are treated as separate but related entities — so if you were to add a message to “Staff” in our previous example, its label would show up as being “Expense Reports/Staff.” The message wouldn’t, however, show up when you click “Expense Reports” in the left-of-screen label list; it’d appear only when you clicked “Staff” in that same section. If you wanted it to appear within the results for both the parent label and the sublabel, you’d have to add both of them onto the message.
6. Use labels for smarter searchesGmail’s labels aren’t just for browsing; you can also use them as variables to narrow down a search and make it faster to find a message you need. To include a label as a variable in a search, just click or tap the Gmail search box at the top of the website or mobile app, type label:work (using the name of your actual label name in place of “work,” of course), and then type in any other term or variable you want.
If you were trying to find a travel-related expense report from Tim Cook’s trip to Chicago, for instance, you could type label:travel from:[email protected] chicago into the search box. Including the label would narrow down your search considerably — skipping over messages from Tim Cook that might’ve just mentioned Chicago in some other context — and let you get to what you need more efficiently.
You can even narrow down your search further and search for messages that contain multiple specific labels — like label:travel label:work, which would show you a list of all messages that have both of those labels in place.
And on the mobile front, you can make your life easier yet by tapping the “Labels” dropdown within the app’s search area. That’ll let you simply select from a list of available options and save yourself the trouble of manually typing anything in.
In the Gmail mobile apps, you can select from a list of existing labels instead of typing in a search.
JR Raphael / Foundry
Gmail actually treats many of its own built-in message designations as labels, too — so in addition to searching for your own custom labels, you can search for (and in some cases also find within the mobile app dropdown menu) things like:
- label:inbox
- label:unread
- label:promotions
- label:social
- label:starred
- label:muted
Beyond that, you’d never know it, but Google also supports a hidden series of advanced Gmail labels for automatically identifying emails related to areas like travel, purchases, and finance.
And finally, any recent past searches you’ve conducted will show up as suggestions whenever you tap or click in the search box, which makes it especially convenient to revisit any frequently accessed label-related explorations in the future.
7. Let Gmail apply labels for youHere’s where things really start to get interesting: In addition to manually applying labels to messages as you see fit, you can train Gmail to automatically categorize and process messages for you.
The first step is to think about what factors would make an incoming message fit into a particular label — whether it’s the sender’s email address or domain name, a specific word or phrase in the subject line, or maybe even the address to which the message was sent.
In my own inbox, for example, Gmail applies a red “VIP” label to emails that arrive from editors or other contacts whose messages tend to be timely and important. And it applies a green “Invoices” label to messages that come in from a specific address and with certain subject lines that my accounting software uses for carbon copies of new invoices.
In some cases, like with the “VIP” label, the messages remain in my primary inbox. But in others, they end up moving to less attention-demanding places — like the invoice copies, which skip over my inbox entirely (since I’m keeping them mostly as records and don’t need to be bothered dealing with them every time they come in).
Once you decide what factors should apply to what label — and what else should happen once the label is applied — a Gmail filter is the key to making the magic happen. I outlined the exact steps to setting one up in my separate Gmail filters guide. Go have at it!
8. Let your labels limit your notificationsLast but not least, instead of getting distracting alerts for every new message that lands in your inbox — or going to the opposite extreme and not getting any email notifications whatsoever — use your Gmail labels as a way to control which messages alert you.
You can pick any label that seems notification-worthy and then limit your notifications only to messages with that label attached. You can even set up label-driven notifications to function on your desktop computer and on your mobile device. (Provided you use Android, that is. Sorry, iPhone folks, but Apple’s garden doesn’t allow this level of customization to fly.)
That’s exactly what I do with my aforementioned “VIP” label, in fact. And it’s actually quite easy to set up. I put together a step-by-step guide here.
And with that, my inbox-dwelling comrade, your label education is complete. Go ahead: Label yourself organized. You’ve earned it.
This article was originally published in November 2019 and most recently updated in September 2026.
Kategorie: Hacking & Security
ZEN.COM mění podmínky už počtvrté od března. Omezuje ZEN Care a upozorňuje na poplatky, které v aplikaci neuvidíte
Litevská platební instituce ZEN.COM, působící i v Česku, během půl roku zveřejnila čtyři nové verze podmínek pro soukromé osoby. Nejdříve změnila adresu a sjednotila označení svých služeb, následně přidala možnost dobíjet účet z banky a také hotovostí. Nejnovější podmínky ale ukazuí i změny méně příznivé pro stávající či nové klienty. ZEN Care už nevyužijete u všech plateb kartou a při rušení účtu po vás může požadovat dodatečné ověření totožnosti.
Kategorie: IT News
- « první
- ‹ předchozí
- 1
- 2
- 3
- 4
- 5
- 6
- 7
- 8
- 9
- …
- následující ›
- poslední »